Security basics for small businesses →
Need a checkup?Checkup Think you've been hacked?Hacked? Tell us about your businessContact

IT and security for small businesses

Blue Tongue sets up the security basics, automates the protections that should run on their own, and gives plain answers when you need them. You get certified help from someone who knows your setup and writes everything down, without the cost of a full-time hire.

Built for small offices and practices of about 1 to 10 people, whether you work from an office, from home or online.

  • Confidential
  • Plain language
  • No obligation

Get a checkup like this for your business. See what's included

Security checkup Example
  • 2-Step VerificationRequired for every user · no text-message codesIn place
  • Email authenticationSPF · DKIM · DMARC p=quarantineIn place
  • Laptop encryptionFileVault on · recovery key stored offlineIn place
  • Admin alertsSuspicious sign-ins emailed to a personIn place
  • Former staff accessAccounts closed the day someone leavesIn place
  • BackupsRunning nightly · restore never testedTo fix
5 of 6 basics in place
Start here

A security checkup for your business

One conversation about the basics that matter most for a small business, then a one-page scorecard you can keep. You'll know what's in place, what isn't, and what to fix first.

$149fixed price

Credited in full toward any follow-up work you book within 60 days.

Other work is $125 an hour, quoted before we start. Our first 10 clients who book by March 31, 2027 get 15% off everything for a year, the checkup included.

Add-ons, quoted at the hourly rate before we start:

  • Access review and offboarding. Who can sign in to what, from admin roles to shared files, plus a written checklist for closing access when someone leaves.
  • AI safety setup. What tools like Gemini or Copilot can see in your files and email, a one-page AI use policy, and settings that keep client and patient information out of AI tools. We help you use AI safely; we don't build AI automations.
  1. A short call

    We go through your accounts, email, devices and backups together. We don't need access to your systems for this.

  2. A one-page scorecard

    Each basic marked "in place" or "to fix", like the example above, in plain language.

  3. Your top three fixes

    Ranked by risk, with what each one takes. Do them yourself or have us do them.

Book a checkup
  • Confidential
  • Plain language
  • No obligation
How it works

From first call to running on its own

Every engagement follows the same four steps, and every change is written down so you always know what was done and why.

  1. Talk

    We learn how your business works, what you use and what worries you.

  2. Assess

    The checkup scorecard first, then a fuller written look at your accounts, email, devices and backups, with the risks ranked.

  3. Fix and automate

    We close the biggest gaps first and set up protections that run without reminders.

  4. Keep it running

    Alerts come to us, records stay current, and you have someone to ask.

Savannah, our mascot, catches bugs before they bite.

Services

What we set up and look after

Each service is tagged with the functions it serves in the NIST Cybersecurity Framework 2.0: Govern, Identify, Protect, Detect, Respond and Recover. Most clients start with accounts and email.

ProtectDetect

Accounts and access

A stolen password alone won't get anyone into your accounts. 2-Step Verification on every account, admin accounts kept separate, and alerts that reach a person when something looks wrong. We also review who can sign in to what, from admin roles to shared files, and close old access when someone leaves.

2SV: required · SMS codes: off
ProtectDetect

Email you can trust

Your mail reaches inboxes, and others can't easily send mail as you, whichever email provider you use. We set up the domain records and read the daily reports with our own open-source DMARC tool, so you don't have to. Sending newsletters through Constant Contact, Mailchimp or Brevo? We make sure those are authenticated too.

v=DMARC1; p=quarantine
IdentifyProtect

Google Workspace

Google Workspace is our specialty. You know who can open what. Accounts, shared drives, devices and settings, set up once and documented so the next person can follow them. We also work with the tools around it, such as Zoom, Dropbox, password managers and your domain host. On Microsoft 365 instead? Ask, and we'll tell you honestly whether we're the right fit.

Admin console · Alert center
Govern

Small medical practices

A HIPAA security risk analysis that protects the practice, not just a checklist for the file, plus written procedures your staff can follow, and a Business Associate Agreement signed before any access to patient systems. Fixed price of $2,000 to $3,000 for practices of up to 10 people at one location, set by practice size and agreed in writing after the checkup.

45 CFR 164.308(a)(1)
GovernProtect

Tax and accounting practices

Federal law requires paid tax preparers to keep a written information security plan. We help you write one that fits a small office, using the IRS's own template, and set up the protections it describes: 2-Step Verification, encryption and safe disposal of old records.

IRS Pub 5708 · FTC Safeguards Rule
ProtectRecover

Devices and backups

A lost laptop doesn't expose your files, and a dead one doesn't lose them. Disk encryption, updates on a schedule, and backups that are tested, not just turned on.

FileVault · BitLocker · restore test
GovernIdentify

Cyber insurance applications

Many cyber insurance applications ask about 2-Step Verification, backups and encryption before they quote. We go through the security questions with you, help you answer them accurately, and fix the gaps they turn up, so your application matches what's really in place. Daniel once assessed business risk as a commercial insurance underwriter, so he knows what those questions are for. We don't sell insurance or advise on coverage.

MFA · backups · encryption
Respond

Help when something goes wrong

You call someone who already knows your setup, for incidents and for the questions that come up between projects.

Plain language, written down
Right now

Think you've been hacked?

Strange emails sent from your account, a ransom note, or a login you don't recognize? Take a breath. Please do these four things first, then get in touch, and we'll help you with the rest.

Email

We reply the same day to suspected security problems (best effort, weekdays 9 am to 5 pm Pacific) and within 2 business days to everything else.

Phone

If patient records may be involved, please say so in your first message, because HIPAA sets deadlines for notifying people.

  1. Don't pay or reply

    If a message demands money, gift cards or crypto, please don't pay and don't answer it. Keep the message so we can look at it together.

  2. Don't wipe anything yet

    Turn off Wi-Fi or unplug the network cable, but leave the computer on and don't reset it. What's on it helps find out what happened.

  3. Change your email password

    Do it from a different device you trust, not the one that may be affected, and turn on 2-Step Verification if it's off.

  4. Contact us

    Tell us what you saw and when; screenshots help. There's no blame here: this happens to careful people too.

About

One person, on your side

Our job is simple: keep the bad guys out of your business, and tell you plainly how we do it.
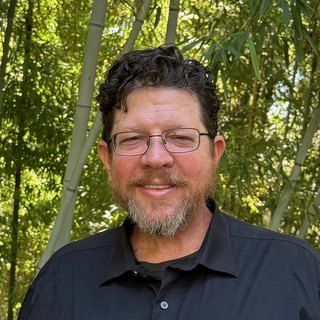
Daniel Harris, owner of Blue Tongue IT & Cyber

Blue Tongue IT & Cyber is run by Daniel Harris in South Pasadena, California. Every client works directly with him, from the first call to the last checkup.

Most work is done remotely by video call. We also come to you across the Los Angeles area, from Pasadena and the San Gabriel Valley to Glendale, Downtown and the Westside. Visits more than 30 miles from South Pasadena include a travel fee, quoted before we go.

That means personal attention: you always reach the same person, and he already knows your setup. It also means Blue Tongue is the right fit for offices of about 1 to 10 people. If you need round-the-clock monitoring or a full help desk, we'll say so and point you to a firm that does that well.

Daniel taught high school science for 18 years, so he explains technical things clearly and patiently. He was also his school's go-to person for tech help, sorting out logins and devices for about 200 students a year. Before teaching, he spent nearly four years designing and managing databases, including who could see which records, then assessed business risk as a commercial insurance underwriter and worked in a quality-control lab. He completed the 400-hour QuickStart cybersecurity bootcamp at UC Santa Barbara and practices in his own home security lab.

CompTIA Security+ (2026) · QuickStart Cybersecurity Bootcamp at UC Santa Barbara (400+ hours) · California teaching credential · M.A. in Education, Cal State LA

  • Written downEvery change is recorded, so you always know what was done and why.
  • Plain languageNo jargon in anything we give you, and we're always glad to explain.
  • Least accessWe ask only for the access a job needs, and for medical practices we sign a Business Associate Agreement before touching patient systems.
  • No surprisesOur prices are on this page, and the price is agreed before the work starts.
  • InsuredWe carry general liability and professional liability (errors and omissions) insurance. A certificate of insurance is available on request.
Contact

Tell us about your business

We'd love to hear from you. Email or call to book a checkup, or send a few lines about your business: how many people, what you use for email and files, and what prompted you to reach out. We reply within 2 business days, and every message is kept confidential.

  • Confidential
  • Plain language
  • No obligation

Email

Phone

Calls and texts reach Daniel directly. If he can't pick up, leave a message and he'll call you back. Please don't include patient or other sensitive details in a text.

Save contact